If your organization builds, sells, or uses AI systems that touch the EU market, the AI Act likely applies to you, whether you’re based in Brussels or Boston. The immediate move is a scope test: determine if you’re a provider or deployer, then run a gap analysis against documentation and risk classification rules before your next system update ships.
TL;DR:
- Accurate classification of AI systems is crucial, as misjudging either high-risk or GPAI models can lead to severe fines and enforcement actions.
- Systems touching areas like hiring, credit, or biometrics require immediate attention for documentation, testing, and human oversight, often taking months to prepare.
- GPAI providers must prepare detailed technical documentation, conduct adversarial testing, and file notifications as thresholds are crossed, with adherence to voluntary codes reducing oversight.
- Enforcement is active, with both the AI Office and national authorities holding investigation powers and penalties reaching up to €35 million or 7% of global turnover for violations.
- Using secure, controlled infrastructure, such as sovereign, air-gapped deployment, simplifies compliance by limiting data flows and reducing audit risks.
Table of Contents
- What Is EU AI Act Compliance and Who Needs It?
- How Do Risk Tiers Change Your Obligations?
- What Documentation Will Auditors Actually Check?
- What Must GPAI Model Providers Do Differently?
- Who Enforces the AI Act, and What Are the Penalties?
- What’s the Fastest Path From Assessment to Compliance?
- How Forge Approaches Operational AI Act Readiness
- Compliance as Ongoing Governance, Not a Checklist
- Get Hands-On Help Deploying a Compliant AI System
- Where to Read the Primary Sources
- Sources
- FAQ
What Is EU AI Act Compliance and Who Needs It?
EU AI Act compliance means meeting the obligations set out in Regulation (EU) 2024/1689, the law establishing risk-based rules for AI systems sold or used in the EU. The Act applies to providers and deployers established in the EU, and to third-country providers whose AI system output gets used within the EU, according to the AI Act Service Desk’s scope guidance. It excludes purely personal, non-professional use and some pre-market research activity.
The provider versus deployer distinction matters more than most legal teams initially assume. A provider builds or substantially modifies a system and places it on the market. A deployer just uses it. One subtle change, like integrating a third-party model into a commercial product instead of running it for internal analytics only, can flip which obligations apply and who faces enforcement exposure.
The rollout happens in stages:
- February 2, 2025: Prohibited practices banned; AI literacy obligations begin.
- August 2, 2025: Governance rules and GPAI obligations take effect.
- August 2, 2026: The Act becomes generally applicable.
- December 2, 2027: High-risk Annex III systems must comply.
- August 2, 2028: High-risk systems embedded in regulated products face full obligations.
Pro Tip: Don’t wait for the latest deadline on your calendar. Systems already in production, especially anything touching hiring, credit, or biometric identification, need attention now because classification work takes months, not weeks.
How Do Risk Tiers Change Your Obligations?
The Act sorts AI systems into four tiers, and each one carries a completely different compliance burden. Getting the classification wrong is the single most common way organizations underestimate their exposure.
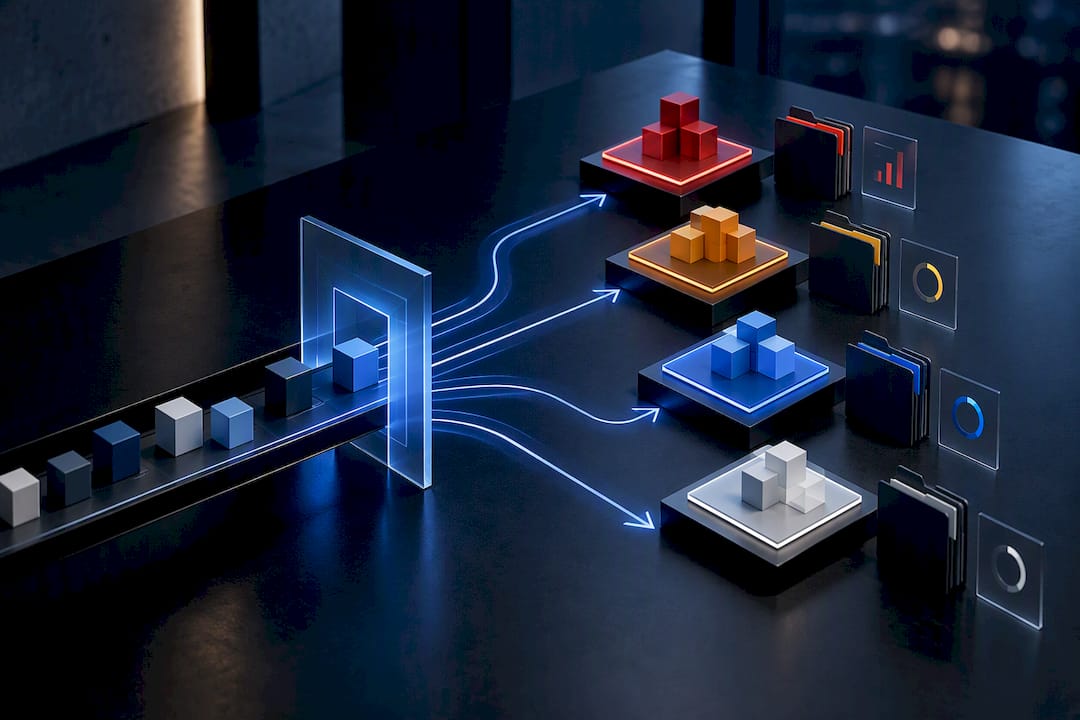
Prohibited practices are banned outright. Social scoring, manipulative subliminal techniques, and most real-time biometric categorization in public spaces fall here. If you’re running one of these, the compliance action is removal, not documentation.
High-risk systems (think hiring algorithms, credit scoring, medical device software) require the heaviest lift:
- Conformity assessment before market placement.
- Full technical documentation and audit trails.
- Registration in the EU database.
- Human oversight mechanisms built into the system design.
Limited-risk systems carry lighter transparency duties. Chatbots must disclose they’re AI. Deepfakes and AI-generated content need clear labeling so users aren’t misled.
General-purpose AI (GPAI) models get their own regime entirely. Once a model qualifies as GPAI, transparency obligations kick in automatically, and models with systemic risk face additional evaluation and reporting duties covered in detail below.
What Documentation Will Auditors Actually Check?
Auditors and the AI Office don’t want a policy binder collecting dust. They want evidence the system works as designed and someone is watching it. Here’s what actually gets checked, roughly in the order it gets checked:
- Risk management records under Article 9. Proportional to the system’s risk tier, updated on a recurring cycle, tied to a named owner rather than a department.
- Technical documentation, including design choices, training data summaries, and system logs going back through the development lifecycle.
- Human oversight evidence, meaning documented checkpoints where a person can intervene, override, or halt the system.
- Accuracy and robustness testing results, especially for anything classified high-risk.
- AI literacy training records, broken out by role. This one surprises a lot of compliance leads.
That last point deserves emphasis. Auditors treat documented AI literacy programs as a real signal of organizational maturity, and missing role-based training is one of the most common audit red flags according to the AI Act Service Desk’s implementation timeline. It’s not a checkbox exercise. Engineers, procurement staff, and frontline deployers each need training scoped to what they actually do with the system.
Pro Tip: Keep training records separate from your general HR compliance files. Regulators want to see AI-specific literacy tied directly to the systems your teams touch, not a generic annual ethics module.
Post-market monitoring closes the loop: log performance drift, track incidents, and report serious malfunctions on a defined schedule rather than after the fact.
What Must GPAI Model Providers Do Differently?
If you provide a general-purpose AI model, Articles 53 and 55 layer on obligations that don’t apply to narrower systems. The baseline requirements under Article 53 include technical documentation for downstream integrators, a public summary of training content, and a documented copyright policy, according to the European Commission’s GPAI obligations guidance.
Models classified as carrying systemic risk face a heavier standard under Article 55:
- Adversarial testing and red-teaming before and after release.
- Cybersecurity measures proportional to the model’s reach.
- Serious-incident reporting to the AI Office within defined timelines.
- Notification once training compute crosses the systemic-risk threshold.
A practical compliance binder for GPAI providers typically holds five things: the public training-content summary using the Commission’s template, documented evaluation and adversarial testing reports, cybersecurity posture evidence, notification records tied to compute thresholds, and downstream-user information packs.
Here’s the part many legal teams miss: the GPAI Code of Practice is voluntary, but signing and implementing it functions as “adequate means” of compliance until harmonized standards exist. Adherence measurably reduces regulatory scrutiny. Skipping it doesn’t mean noncompliance, but it does mean carrying the full burden of proof yourself.
Who Enforces the AI Act, and What Are the Penalties?
The AI Office enforces GPAI obligations directly, while national competent authorities in each member state handle enforcement for other AI systems deployed in their territory. Both bodies can issue requests for information, demand access for model evaluations, and impose corrective measures.
The fines scale with the violation:
- Prohibited practices: up to €35 million or 7% of worldwide annual turnover, whichever is higher.
- GPAI obligation breaches: up to €15 million or 3% of worldwide annual turnover.
- Other infringements: penalties vary by member state and violation type.
The AI Office treats GPAI providers as a priority enforcement target and expects proactive engagement, not silence until a complaint arrives. Signing the Code of Practice, maintaining open technical dialogue, and documenting remediation steps as you find gaps all reduce the odds of an intrusive investigation.
What’s the Fastest Path From Assessment to Compliance?
A workable roadmap runs in five steps, roughly matching how legal, compliance, and engineering teams should sequence the work over three to six months.
- Run a scope test. Determine provider versus deployer status for each system and name a compliance owner, not a committee.
- Classify every system by risk tier. Prioritize anything that looks high-risk or GPAI first; everything else can wait.
- Run a gap analysis against required technical documentation and AI literacy training records.
- Build the operational controls: logging, human oversight checkpoints, and monitoring dashboards tied to specific systems.
- For GPAI providers, prepare the public training summary, complete model evaluations, and file notifications once compute thresholds are met.
Note that the AI Omnibus, which entered into force on July 27, 2026, introduced proportionality measures for smaller organizations and expanded regulatory sandboxes, so SMEs shouldn’t assume the full documentation burden applies identically to them.
Pro Tip: Assign artifacts, not just tasks. “Documentation owner: Sarah, artifact: technical file v2, due: Q3” gets audited well. “Compliance team will handle documentation” does not.
How Forge Approaches Operational AI Act Readiness
Compliance work gets harder when data leaves your infrastructure to reach a model. Forge AI Deployment’s air-gapped deployment approach sidesteps that problem by design, since data never leaves your controlled environment in the first place. That structurally reduces the documentation burden around data flows that auditors scrutinize most closely.
Forge’s services map directly onto the operational tasks above:
- Local, sovereign deployment that keeps training and inference data inside client infrastructure.
- Sovereign MLOps and runtime orchestration to support the logging and monitoring auditors expect.
- Custom model integration built on the webAI platform, Forge’s technology partner for sovereign deployments.
- Documentation and performance tuning support drawing on 20 years of experience securing sensitive operations.
Organizations should still validate their own risk classification and legal obligations with qualified counsel; the role of some providers is the technical deployment layer underneath that governance work.
Compliance as Ongoing Governance, Not a Checklist
Treating the AI Act as a one-time filing exercise misses the point entirely. The organizations that handle this well embed roles, evidence collection, and training into normal operations, not into a folder someone opens once a year.
Early, documented engagement with regulators when something goes wrong beats silence every time. Remediation you can show is worth more than a clean record you can’t prove.
John covers AI governance and enterprise security topics, focusing on how organizations operationalize regulatory requirements inside real technical infrastructure.
— John Ezzell, Founder
Get Hands-On Help Deploying a Compliant AI System
Reading the regulation is one thing. Building a system that keeps your data inside your own walls while still meeting documentation and oversight requirements is another. Forge is the alternative to sending sensitive data through a third-party cloud model: your organization keeps full control of data, models, and logs inside infrastructure you own, which directly supports the technical documentation and human oversight evidence regulators ask for.
Forge’s solutions cover secure local and air-gapped deployment, custom model integration, private AI assistant rollout, sovereign MLOps, and ongoing performance tuning, priced through direct engagement rather than software licensing. If your team needs a readiness assessment or wants to see how a sovereign deployment fits your compliance timeline, start a conversation with Forge about your next system rollout.
Where to Read the Primary Sources
For the exact legal language and official guidance, go straight to the source rather than secondhand summaries:
- Regulation (EU) 2024/1689: the official AI Act text.
- AI Act Service Desk: implementation timeline and GPAI guidance.
- European Commission enforcement page: AI Office powers and penalty structure.
Compliance professionals working through regulated environments outside AI specifically may also find useful parallels in 21 CFR Part 11 compliance patterns, which share similar documentation and audit-trail logic.
Sources
- AI Act Service Desk — timeline implementation
- Enforcement of the AI Act (European Commission)
- AI Act Service Desk — Article 2 (scope)
- General-Purpose AI Models — Questions & answers (European Commission)
FAQ
Does the EU AI Act Apply to the US?
Yes, if a US company’s AI system output is used within the EU, the Act applies regardless of where the company is headquartered. This third-country coverage is one of the most misunderstood parts of the scope rules, and it catches many American software vendors off guard.
Is the EU AI Act Being Enforced?
Enforcement is active and phased in alongside the implementation timeline, with prohibited practices already banned since February 2025 and full applicability from August 2026. The AI Office and national authorities both hold investigative and fining powers today, not just after every deadline passes.
Is the EU AI Act Mandatory?
Yes, it’s binding law across the EU, not a voluntary framework, with fines reaching €35 million or 7% of global turnover for the most serious violations. The one genuinely voluntary piece is the GPAI Code of Practice, which organizations can adopt to demonstrate adequate compliance.
Who Regulates the EU AI Act?
The AI Office handles enforcement for general-purpose AI model providers, while national competent authorities in each member state enforce obligations for other AI systems operating in their territory. Both can issue information requests, demand model access for evaluation, and impose corrective measures or fines.
How Can Organizations Reduce Their Compliance Risk?
Running a scope test early, classifying systems by risk tier, and maintaining documented AI literacy training are the fastest ways to reduce exposure. Deployment choices matter too. Keeping data and models inside controlled infrastructure, the approach Forge builds around, removes several data-flow risks that auditors focus on first.